You put your money into a liquidity pool, expecting steady yield. Then, in seconds, the price crashes, or worse, the funds vanish. It wasn't bad luck; it was an exploit. Automated Market Makers (AMMs) revolutionized trading by removing order books, but they introduced a new playground for hackers. If you're interacting with decentralized exchanges, understanding AMM vulnerabilities isn't optional-it's survival.
The Core Mechanics of AMM Risk
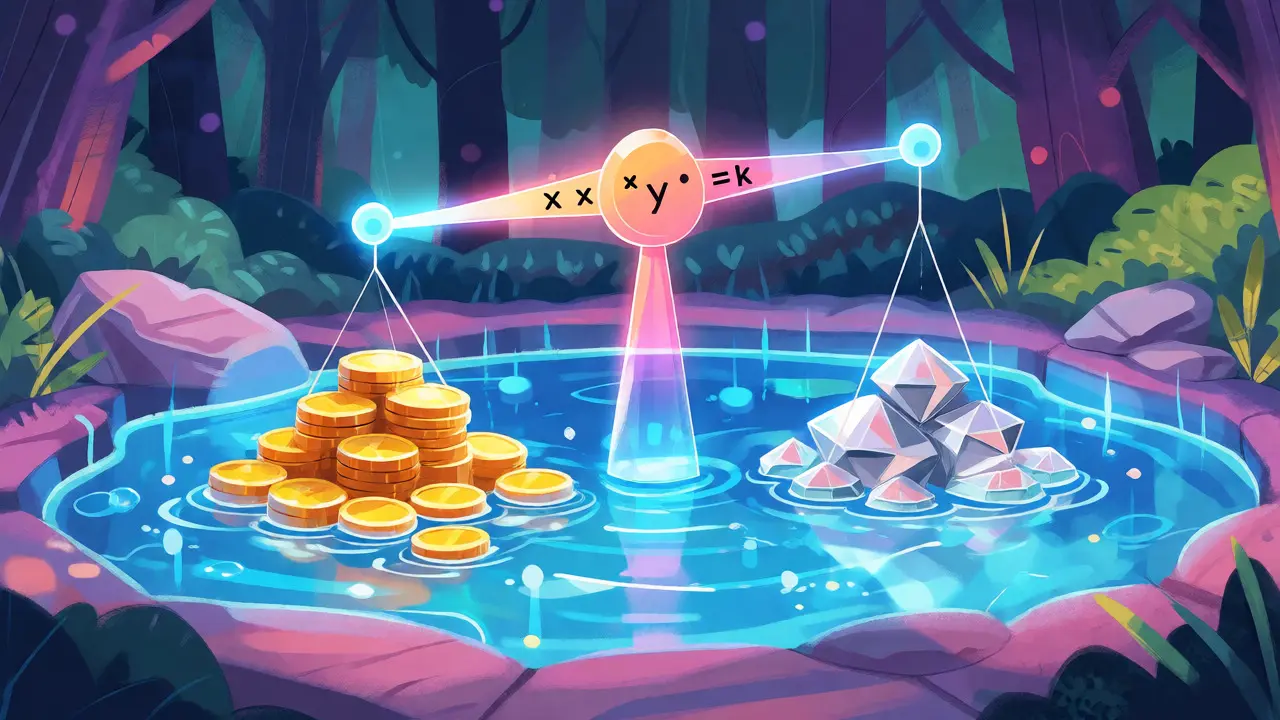
Before we look at the hacks, let's clarify what we are protecting. An Automated Market Maker is a type of decentralized exchange protocol that relies on mathematical formulas to determine asset prices rather than traditional order books. Unlike centralized exchanges where buyers and sellers match orders, AMMs use liquidity pools funded by users. The most famous formula, used by Uniswap V2, is $x \times y = k$. This constant product model means if one asset decreases in quantity, its price must increase to keep the product constant.
This deterministic pricing creates specific attack surfaces. Because the price is derived from the ratio of assets in the pool, any manipulation of those ratios affects the price instantly. Hackers don't need to convince a market maker to change their mind; they just need to move enough capital to skew the math. This is fundamentally different from traditional finance risks. In DeFi, code is law, and if the code has a gap, the money leaves.
Flash Loan Attacks: The Instant Heist
Imagine borrowing ten million dollars without collateral, using it to manipulate a market, paying it back, and keeping the profit-all within one transaction block. That's a Flash Loan is an uncollateralized loan that must be borrowed and repaid within the same blockchain transaction block. Platforms like Aave and dYdX enable this. While legitimate traders use them for arbitrage, attackers use them for exploitation.
In a typical flash loan attack, the attacker borrows a large amount of Asset A. They swap it into Asset B, draining the liquidity pool and artificially inflating the price of Asset B. Because many protocols rely on spot prices from these pools for liquidations or oracle feeds, this price spike triggers other actions. The attacker might trigger a liquidation on their own debt, buy back Asset A at the inflated price, repay the flash loan, and pocket the difference. The victim? Often the protocol itself or other liquidity providers who suffer from severe Impermanent Loss is the temporary reduction in value experienced by liquidity providers when the price of deposited assets changes compared to when they were deposited.
Sandwich Attacks and MEV
Have you ever tried to buy a token and got a terrible price, only to see the price recover immediately after? You likely became a victim of a sandwich attack. This falls under the broader umbrella of Maximal Extractable Value (MEV) is the maximum value that can be extracted from block production in excess of the standard block reward and gas fees by including, excluding, and changing the order of transactions in a block.
Here is how it works: A bot monitors the mempool (the waiting area for pending transactions). It sees your large buy order. The bot places its own buy order before yours, driving up the price. Your transaction executes at this higher price. Then, the bot sells its tokens immediately after your transaction, profiting from the price impact you caused. You pay more for less; the bot takes the spread. This isn't a bug in the AMM code per se, but a vulnerability in the transparency of the blockchain. Since everyone can see pending trades, sophisticated actors can front-run you.
Oracle Manipulation: The Price Feed Trap
Many lending protocols and derivatives platforms don't trade directly on AMMs. Instead, they ask, "What is the current price of ETH?" They get this answer from an oracle. If the oracle uses a simple spot price from a single AMM pool, it is vulnerable. Attackers can manipulate that specific pool's price via flash loans, as described above. The oracle reports this manipulated price to the lending protocol. The protocol then allows the attacker to borrow against overvalued collateral or liquidate others based on fake data.
Robust protocols mitigate this by using time-weighted average prices (TWAPs) or aggregating data from multiple sources. However, older or cheaper protocols often cut corners here. When auditing a project, always check how it derives price data. If it relies on a single source of truth from a small liquidity pool, it's a ticking time bomb.
Smart Contract Bugs and Reentrancy
Beyond economic exploits, there are pure coding errors. One of the most notorious is the reentrancy attack. Imagine a smart contract function that sends Ether to a user before updating the internal balance. A malicious contract receiving the Ether can call the withdrawal function again before the first execution finishes, effectively withdrawing its funds multiple times. The DAO hack in 2016 was a classic example, though not strictly an AMM issue, the logic applies to AMM interfaces.
Another common issue is rounding errors. In integer-based systems like Ethereum's Solidity, division results are truncated. If an AMM rounds down too aggressively during swaps, dust accumulates. Over thousands of transactions, this can lead to significant discrepancies in the pool's reserves versus the expected mathematical state. While usually minor, in high-frequency trading environments, these micro-leaks add up.
Comparing Common AMM Exploit Types
| Vulnerability Type | Mechanism | Primary Target | Mitigation Strategy |
|---|---|---|---|
| Flash Loan Attack | Borrow massive capital to manipulate pool ratios temporarily. | Lending Protocols, Oracles | Use TWAP or multi-source oracles. |
| Sandwich Attack | Front-running and back-running user transactions for profit. | Retail Traders | Set slippage limits; use private RPCs. |
| Reentrancy | Recursive calling of functions before state updates. | Smart Contracts | Checks-Effects-Interactions pattern. |
| Oracle Manipulation | Feeding false price data to dependent protocols. | Derivatives, Lending | Decentralized oracle networks (e.g., Chainlink). |
How to Protect Your Liquidity
So, what do you actually do? First, look at the Total Value Locked (TVL) and audit history. A protocol with millions in TVL and no public audits is risky. Second, understand the tokenomics. Is the liquidity deep enough to resist manipulation? A pool with $10k liquidity is easily moved by a $5k trade. A pool with $10M requires much more capital to skew.
Third, manage your slippage tolerance. Setting it too low might cause failed transactions, but setting it too high exposes you to sandwich attacks. A good rule of thumb for volatile pairs is 1-2%, but adjust based on volatility. Fourth, consider using tools that offer private transactions. Services like Flashbots or specific wallet features can hide your transaction from the public mempool until it is mined, preventing bots from seeing and attacking your trade.
The Future of AMM Security
The landscape is evolving. Newer AMM designs, like Uniswap V3, introduce concentrated liquidity. This increases capital efficiency but also concentrates risk. If all liquidity is in a narrow price range, a large sell-off can exit the range entirely, leaving the pool empty and causing extreme price impacts. Developers are also experimenting with intent-based architectures, where users sign an intention to trade, and solvers compete to fill it. This shifts the power dynamic away from the mempool and reduces sandwich attack opportunities.
Security is not a destination; it's a continuous arms race. As long as there is profit to be made, there will be someone trying to extract it through cleverness or code flaws. Stay skeptical, verify contracts, and never invest more than you can afford to lose to a zero-day exploit.
What is the difference between impermanent loss and an exploit?
Impermanent loss is a natural economic outcome of providing liquidity when asset prices diverge; it is not a bug. An exploit is a security failure where an attacker leverages a code flaw or market mechanism to steal funds or distort prices unfairly. Impermanent loss is predictable math; exploits are unexpected failures.
Can I prevent sandwich attacks completely?
You cannot prevent them entirely on public chains like Ethereum, but you can significantly reduce risk. Use private transaction relayers (like Flashbots), set strict slippage tolerances, and avoid trading large amounts in low-liquidity pools during high-volatility periods.
Are flash loans inherently dangerous?
No, flash loans are neutral financial instruments. They are essential for efficient arbitrage and liquidity rebalancing. They become dangerous when protocols rely on instantaneous spot prices for critical decisions, allowing attackers to manipulate those prices temporarily with borrowed capital.
Why do audited projects still get hacked?
Audits cover known patterns and common bugs at a point in time. They may miss complex economic interactions between different protocols (composability risks). Additionally, upgrades to smart contracts after the audit can introduce new vulnerabilities if not properly tested.
What is MEV and why does it matter to me?
MEV (Maximal Extractable Value) is the profit miners or validators make by reordering transactions. For you, it means your trade might execute at a worse price because a bot inserted its own trade before yours. It matters because it acts as a hidden tax on DeFi users.