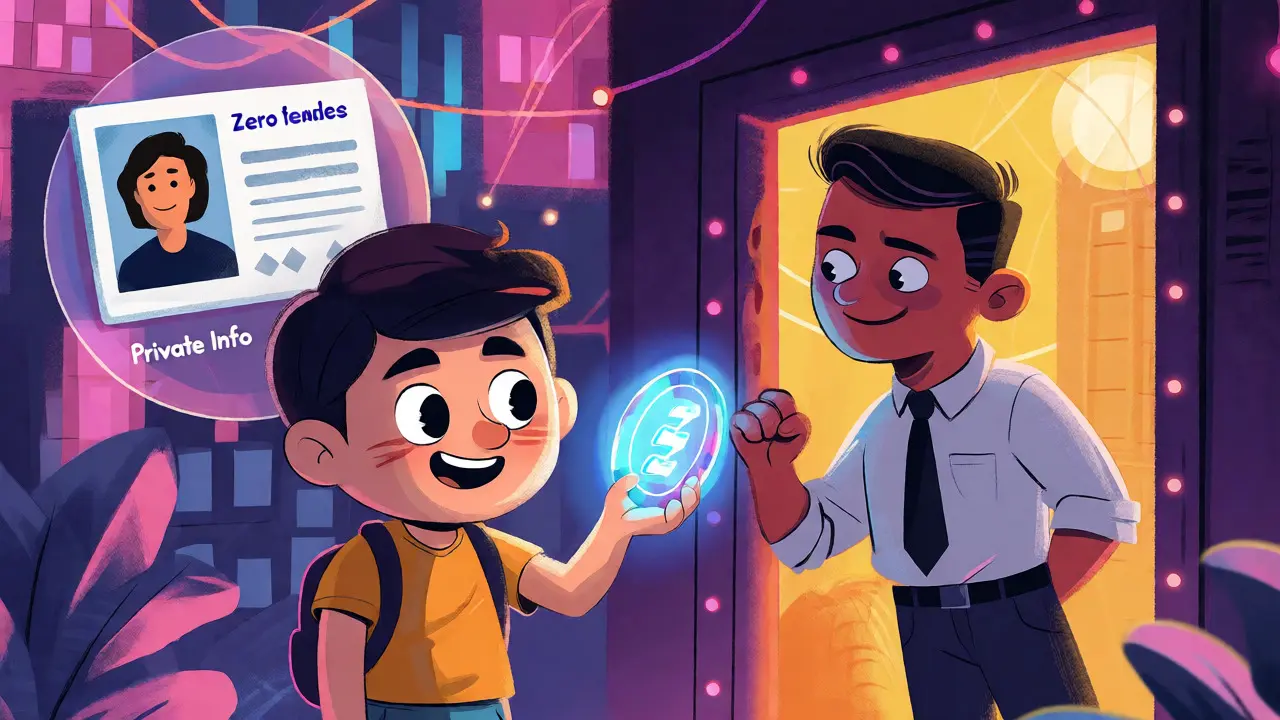
Imagine you want to prove to a bouncer that you’re over 21 without showing them your driver’s license. You don’t hand over the card; you just show a digital token that says "Yes." The bouncer knows you’re old enough, but they never see your name, address, or birth date. That is the core idea behind Zero-Knowledge Proofs (ZKPs). In the world of cryptocurrency and blockchain technology, this cryptographic method allows one party (the prover) to convince another (the verifier) that a statement is true, without revealing any information beyond the fact that it is true.
This isn’t just theoretical magic. It’s the engine driving some of the biggest shifts in crypto today. If you’ve ever wondered how coins like Zcash hide transaction amounts, or why Ethereum layer-2 networks like zkSync can process thousands of transactions per second while staying secure, ZKPs are the answer. They solve two massive problems at once: privacy and scalability. By the end of this guide, you’ll understand exactly how they work, where they’re used, and why they matter for the future of money.
The Core Concept: Proving Without Revealing
To grasp ZKPs, forget complex math for a second. Think about trust. In traditional systems, we trust banks or governments to verify our identity or balance. In crypto, we trust the blockchain ledger. But sometimes, you need to prove something specific without opening your whole book. For example, proving you have enough Bitcoin to pay for coffee, without revealing your total wallet balance.
A valid Zero-Knowledge Proof must satisfy three strict properties:
- Completeness: If the statement is true, an honest verifier will be convinced by an honest prover. No false negatives.
- Soundness: If the statement is false, no cheating prover can convince the honest verifier that it is true. No false positives.
- Zero-Knowledge: If the statement is true, no verifier learns anything other than the fact that the statement is true. This is the key differentiator from standard cryptography.
The concept was formally introduced in 1985 by researchers Shafi Goldwasser, Silvio Micali, and Charles Rackoff. But it didn’t hit mainstream crypto until the Zerocoin protocol in 2013, which later evolved into Zcash. Today, it’s foundational infrastructure, not just a niche feature.
How Do They Actually Work?
Under the hood, ZKPs rely on advanced mathematics, specifically elliptic curve cryptography and polynomial commitments. But here’s the simplified flow:
- The Circuit: Developers write the logic of what needs to be proven as a mathematical circuit. Think of this as a series of gates (like AND/OR gates in electronics) that take inputs and produce outputs.
- The Witness: The prover provides secret data (the "witness") to the circuit. For a transaction, this might be your private key and the amount being sent.
- The Proof Generation: The prover runs the witness through the circuit. Using a specialized algorithm, they generate a short proof-a string of bytes-that attests the calculation was done correctly.
- Verification: The verifier checks the proof against public parameters. If the math holds up, the transaction is valid. Crucially, the verifier never sees the private key or the exact input values if they are hidden.
This process happens in milliseconds. For instance, verifying a zk-SNARK proof takes only 3-10 milliseconds on standard hardware. That speed is critical for blockchains that need to confirm transactions quickly.
Types of ZKPs: SNARKs vs. STARKs vs. Bulletproofs
Not all zero-knowledge proofs are created equal. Different projects use different types based on their priorities-speed, size, or trust assumptions. Here’s a breakdown of the main players:
| Feature | zk-SNARKs | zk-STARKs | Bulletproofs |
|---|---|---|---|
| Primary Use Case | Zcash, zkSync, StarkNet | StarkNet, Ethereum L2s | Monero |
| Trusted Setup | Required | Not Required | Not Required |
| Proof Size | Very Small (~288 bytes) | Larger (~45 KB) | Medium (varies) |
| Verification Speed | Fastest | Slower | Moderate |
| Quantum Resistance | No | Yes | No |
zk-SNARKs (Zero-Knowledge Succinct Non-Interactive Arguments of Knowledge) are the most famous. They produce tiny proofs that are cheap to verify. The catch? They require a "trusted setup." This means a group of people had to generate initial parameters and then destroy their secrets. If anyone kept their piece of the puzzle, they could theoretically forge proofs. Zcash handled this with a multi-party ceremony involving six people across six countries.
zk-STARKs (Scalable Transparent Arguments of Knowledge) remove the trusted setup requirement, making them more transparent and quantum-resistant. However, their proofs are much larger, which costs more gas fees on chains like Ethereum. They are favored by projects like StarkNet that prioritize security assumptions over minimal proof size.
Bulletproofs are used by Monero. They don’t need a trusted setup and offer smaller proof sizes than early ring signatures. While they aren’t strictly "SNARKs," they achieve similar zero-knowledge goals for range proofs (proving a number is within a certain range, like ensuring a transaction amount is positive).
Why Crypto Needs ZKPs: Privacy and Scaling
You might ask, "Why bother with this complexity?" The answer lies in two major bottlenecks: privacy leaks and network congestion.
Privacy Protection: On Bitcoin, every transaction is public. Anyone can trace funds from Alice to Bob. With ZKPs, you can hide the sender, receiver, and amount. Zcash offers "shielded" transactions where these details are encrypted using zk-SNARKs. Only the parties involved hold the keys to decrypt the details. This brings digital cash closer to physical cash, where handing someone a $20 bill doesn’t reveal your bank balance.
Layer-2 Scaling: Ethereum is slow and expensive. Layer-2 solutions called "Rollups" batch hundreds of transactions off-chain and submit a single proof to the main chain. Instead of verifying 1,000 individual signatures, Ethereum verifies one ZK-proof that says, "I checked all 1,000 transactions, and they were valid." This reduces gas costs by 80-90%. According to L2BEAT data, ZK-Rollups like zkSync Era have processed millions of dollars in value with significantly lower fees than the base layer.
Real-World Applications Beyond Privacy
While privacy gets the headlines, ZKPs are doing much more. They are becoming essential for interoperability and identity.
Interoperability: How do you move assets between two different blockchains securely? Light clients usually download headers from one chain to verify state on another. With ZKPs, you can create a "ZK-Light Client" that verifies the entire state of a blockchain with a small proof. This makes cross-chain bridges safer and cheaper.
Identity Verification: Imagine logging into a service by proving you are a member of a specific DAO or that you passed a KYC check, without revealing your passport number. Projects like Worldcoin and various decentralized identity protocols use ZKPs to allow users to share credentials selectively. You prove you are over 18, not that you are born on January 1, 1990.
Enterprise Finance: JPMorgan’s Onyx division uses ZKPs for its JPM Coin settlement system. Banks need to settle trades quickly but often cannot reveal proprietary trading strategies or client balances publicly. ZKPs allow them to prove solvency and transaction validity on a shared ledger without exposing sensitive business data.
Challenges and Limitations
ZKPs aren’t a silver bullet. There are real hurdles developers and users face.
Complexity: Writing ZK circuits is hard. Developers need to understand finite field arithmetic and low-level programming languages like Circom or Cairo. The learning curve is steep, often taking 6-9 months to become proficient. This slows down innovation compared to writing simple Solidity contracts.
Proving Time: While verification is fast, generating the proof can be computationally heavy. For complex smart contracts, creating a proof might take seconds or even minutes. This requires powerful hardware, leading to concerns about centralization if only large companies can afford efficient provers.
Metadata Leakage: Even if the transaction content is hidden, timing and graph analysis can sometimes deanonymize users. If Alice sends 5 ZEC to Bob at the exact same time Carol sends 5 ZEC to Dave, observers might guess who paid whom. Privacy tools help, but they aren’t perfect.
The Future: Where Is This Heading?
The trajectory is clear: ZKPs are moving from niche to foundational. Vitalik Buterin has projected that ZK-EVMs (Ethereum Virtual Machines compatible with ZK proofs) will handle over 50% of Ethereum transactions by 2027. This would dramatically reduce congestion and make Ethereum usable for everyday applications.
We are also seeing hardware acceleration. Companies are designing specialized chips just for generating ZK proofs, aiming to cut generation times further. Meanwhile, regulatory bodies like the FATF are updating guidelines to accommodate privacy tech, recognizing that ZKPs can actually aid compliance by allowing auditors to verify rules without seeing raw data.
For investors and developers, understanding ZKPs is no longer optional. Whether you are looking at Zcash for privacy, zkSync for scaling, or emerging projects in decentralized identity, the underlying tech is the same. It’s the cryptographic glue holding together the next era of scalable, private, and interoperable blockchains.
Are Zero-Knowledge Proofs safe?
Yes, they are considered highly secure when implemented correctly. The mathematical foundations (elliptic curves and hash functions) are robust. However, implementation bugs can occur. For zk-SNARKs, the "trusted setup" phase is a potential vulnerability if participants didn't properly destroy their secret keys, though ceremonies like Zcash's Powers of Tau mitigate this risk effectively.
What is the difference between zk-SNARKs and zk-STARKs?
The main differences are trusted setup and proof size. zk-SNARKs require a trusted setup and have very small proof sizes (bytes), making them cheap to verify. zk-STARKs do not require a trusted setup and are quantum-resistant, but they have much larger proof sizes (kilobytes), which increases storage and bandwidth costs.
Do ZKPs make transactions completely anonymous?
They provide strong privacy, but not necessarily complete anonymity. ZKPs hide the *content* of the transaction (sender, receiver, amount). However, metadata such as transaction timing, IP addresses, and interaction patterns can still be analyzed. True anonymity often requires combining ZKPs with other techniques like mixers or ring signatures.
Which cryptocurrencies use Zero-Knowledge Proofs?
Major examples include Zcash (uses zk-SNARKs for shielded transactions), Monero (uses Bulletproofs for range proofs), and various Ethereum Layer-2 solutions like zkSync, StarkNet, and Scroll (use ZK-Rollups for scaling). Many newer blockchains are also integrating ZKPs natively.
Why are ZK-Rollups better than Optimistic Rollups?
ZK-Rollups use cryptographic proofs to validate transactions immediately, meaning withdrawals are instant. Optimistic Rollups assume transactions are valid unless challenged, requiring a 7-day waiting period for withdrawals to allow for fraud proofs. ZK-Rollups also generally offer higher throughput and lower finality times.